Choosing to watch loads a YouTube player. Watch on YouTube instead ↗
- When
- November 2, 1988
- Who
- Robert Tappan Morris, a Cornell grad student
- Reach
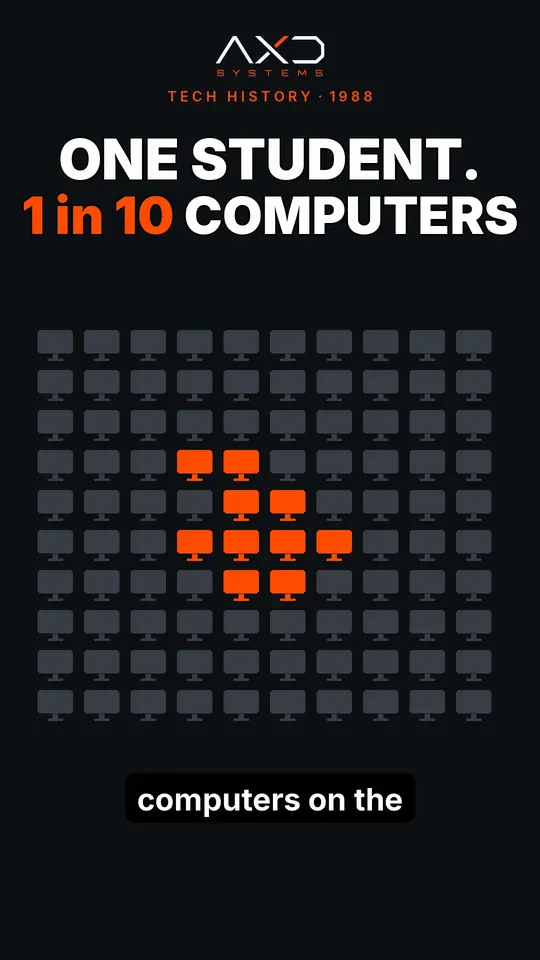
- About 6,000 computers, about 1 in 10 online
- Result
- First conviction under the U.S. computer fraud law
An experiment that got away
On November 2, 1988, Cornell graduate student Robert Tappan Morris released a small program onto the internet. It was meant to spread quietly, but a flaw made it copy itself again and again, even onto machines it had already infected. Computers slowed to a crawl and crashed.
Within about a day, the Morris worm had hit roughly 6,000 machines, about 1 in 10 computers on the internet at the time. Morris became the first person convicted under the U.S. Computer Fraud and Abuse Act. The incident also led to the creation of the first computer emergency response team, CERT, to coordinate fixes.
The cheapest security you’ll ever buy
- Turn on automatic updates. On every computer and phone, for the operating system and your browser.
- Don’t forget the router. Wi-Fi routers and printers need firmware updates too, and old ones may never get them again.
- Replace what’s out of support. If a device or program no longer gets security updates, plan to replace it before it becomes the open door.
New weird tech history every Friday, in about 20 seconds.
Subscribe on YouTube ↗More weird tech history
Want a second set of eyes on your tech?
Run our free Tech Checkup, or book a free 30-minute consultation.